What to know
- Citrix reports targeted exploitation causing denial of service.
- Exposure depends on Gateway or AAA deployments using SAML.
- Earlier fixes do not cover the newly disclosed vulnerability.
A fresh advisory changes the patch baseline
Citrix has disclosed CVE-2026-88779, a memory overflow affecting customer-managed NetScaler ADC and Gateway deployments using SAML with Gateway or AAA functionality. The company reports targeted attacks that can disrupt availability. It recommends 14.1-73.41, 13.1-64.28 and corresponding FIPS releases, including 13.1-37.282 for FIPS and NDcPP. Organizations that installed the preceding security updates must upgrade again if the new preconditions apply.
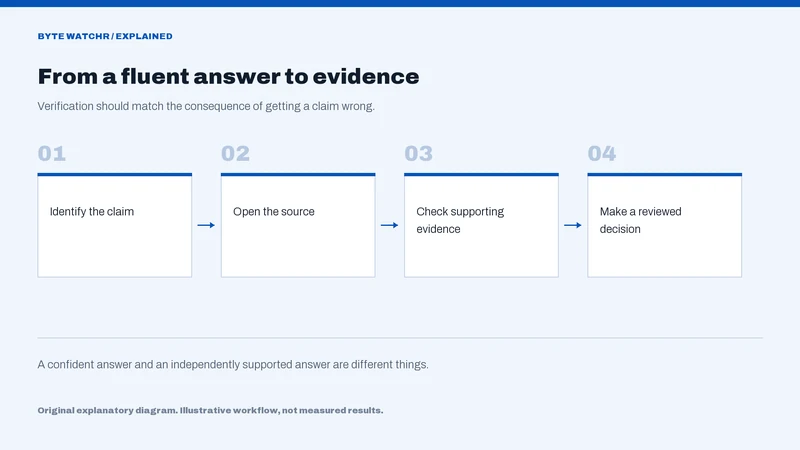
The immediate operational problem is that a recent maintenance window can create false confidence. A dashboard that records only whether an appliance was patched this week cannot answer whether it runs the currently recommended release. Response teams need the exact installed build, authentication configuration and service role for every exposed appliance. That evidence is more useful than a general assurance that the perimeter has already been addressed.
Source: Citrix security guidance
Analysis: Authentication outages have a wider blast radius
An authentication gateway sits between users and the services they need. Repeated interruption can prevent remote staff from reaching business applications even when those applications remain healthy. Organizations should therefore assess the dependency chain behind the appliance: identity providers, emergency access paths, administrative consoles and support workflows. A redundant gateway is useful only if the alternative has been patched and can actually handle the required authentication load.
The vendor’s confirmed description concerns availability. Teams should preserve that distinction when briefing executives and customers. Reports of more severe outcomes require separate verification; they should not be presented as established facts merely because a memory bug could theoretically support them. Equally, the absence of a confirmed integrity impact is not a reason to discard logs or skip the organization’s incident process when suspicious activity appears.
What administrators need to verify
A useful remediation record should include configuration applicability, the chosen supported release, upgrade completion and a post-change authentication test. Test ordinary user access and privileged administration separately. Check that failover peers have matching protection and that an old standby cannot reintroduce the vulnerable version during recovery. Retain relevant logs before rotation removes evidence from the period of suspected attacks.
Citrix offers deny-list mitigation, but an interim filter should have an owner and an expiration condition. Otherwise a temporary measure can quietly become the permanent security posture. Recovery exercises should also confirm that emergency access does not depend on the same failing authentication path. The central lesson is practical: patch work is complete only against the latest applicable advisory, with the service tested afterward. In a fast-moving exploitation wave, yesterday’s successful upgrade can become today’s new action item.
Sources & further reading
Factual statements are grounded in the linked material. Interpretation and illustrative examples are Byte Watchr analysis. Vendor claims are identified as claims, rather than independent testing.
The event date records the source announcement or documented operation. The coverage edition groups recent developments and is separate from the publication date. Actual publication is recorded above.
Corrections policy · About this byline