What to know
- Treat network administration as a distinct security boundary.
- Preserve evidence that can explain configuration and access changes.
- Use the 2024 guidance as a historical lesson, not evidence of a new incident.
Put the guidance in its historical setting
On December 3, 2024, a group of international agencies published Enhanced Visibility and Hardening Guidance for Communications Infrastructure. The document followed identified compromises of major telecommunications providers by actors affiliated with the People’s Republic of China. The FBI’s April 2025 account identifies the associated campaign as Salt Typhoon and links back to that guidance. This article examines those historical publications, not a newly reported compromise.
The lasting question is how a provider can distinguish authorized operation from an adversary exercising useful access. A communications service may continue to carry traffic while parts of its administration require investigation. Availability is one observation about a network. It does not establish that configuration, credentials, or the systems used to manage that network remain under exclusive authorized control.
Source: Joint Guidance: Enhanced Visibility and Hardening for Communications Infrastructure, December 3, 2024 · FBI: PRC Targeting of U.S. Telecommunications, April 24, 2025
Draw the management path separately
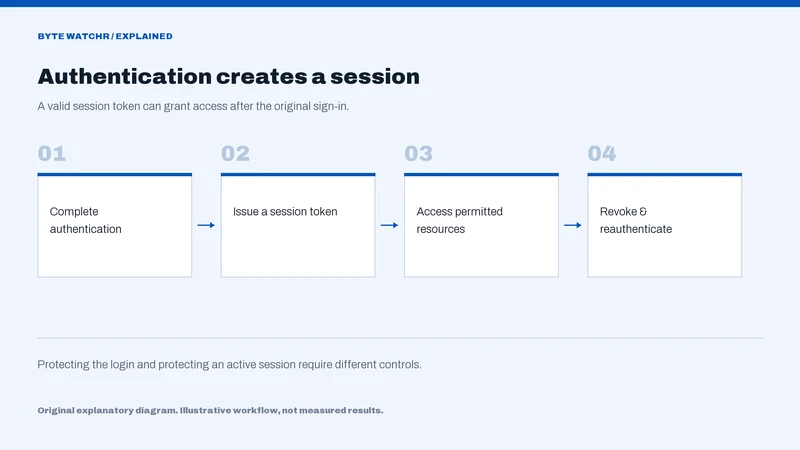
The December guidance recommended an isolated management network and strict controls on administrative access. Treat that recommendation as a design question with an observable answer. Which devices can initiate administration, which identities can use them, and which destinations are reachable? A diagram should show those paths separately from ordinary customer traffic and from general employee access.
Consider a hypothetical regional provider whose engineer changes a router configuration through a shared operations environment. Trace the entire route, including the engineer’s login, the management workstation, the device interface, and any automation account. If several teams describe different routes, that disagreement is a finding. The boundary cannot be assessed confidently while its owners disagree about where it runs.
Make a change explain itself
A legitimate configuration change should have enough surrounding evidence to be understandable later. In the hypothetical provider, a reviewer should be able to connect an approved maintenance task to the responsible identity, the configuration difference, and the affected device. This does not require every change to follow an identical workflow. It requires the organization to know which workflow actually authorized the change.
Suppose a permitted change appears during the right maintenance window but touches an additional device. The calendar alone cannot explain that difference. Compare the approved scope, independent configuration records, and access evidence. If those records are incomplete, describe the resulting uncertainty explicitly. Absence of a recorded exception is not proof that every observed action belonged to the approved task.
Keep the evidence outside the same failure
The joint guidance emphasized visibility into network behavior and configuration. The practical extension is to examine whether the evidence depends entirely on the system being investigated. A configuration archive, for example, provides less independent reassurance when the same administrative authority can alter both the live device and every retained copy without a separate record.
Run a controlled exercise using an authorized, low-impact maintenance action. Confirm that another team can reconstruct what happened from the retained evidence. Record clock differences, missing fields, and devices that cannot provide the expected detail. These gaps determine which conclusions an investigation could support. A dashboard that looks comprehensive may still be unable to answer a narrow, consequential question.
Describe what each protection can establish
Security discussions become imprecise when every concern is described as intercepting communications. Customer content, connection records, administrative access, and configuration integrity are different questions. A review should identify the information or authority at issue before selecting a control. The FBI’s historical description of the campaign provides context, but it does not establish what any particular organization has experienced.
In the provider example, a stronger administrative login can reduce one access risk while leaving an overly broad automation account untouched. A protected customer application may address content confidentiality without proving that network administration is trustworthy. Write down the claim each control supports and the claims it leaves unresolved. This helps technical teams avoid offering a single reassuring answer to several different problems.
Source: FBI: PRC Targeting of U.S. Telecommunications, April 24, 2025
Turn the lesson into a bounded review
Begin with one important management path, identify its owner, verify its permitted use, and test whether authority can be withdrawn. Review emergency access alongside routine access, because an exception that nobody can explain undermines the normal design. Coordinate changes with network operations and test their effect on the provider’s ability to maintain service.
The useful outcome is a defensible account of who can change the network and how that change becomes visible. The 2024 guidance supplies a historical reason to ask those questions. The organization must supply the local evidence. That distinction keeps the review practical and prevents an analysis of a documented campaign from becoming an unsupported claim about a present compromise.
Sources & further reading
- Joint Guidance: Enhanced Visibility and Hardening for Communications Infrastructure, December 3, 2024
- FBI: PRC Targeting of U.S. Telecommunications, April 24, 2025
Factual statements are grounded in the linked material. Interpretation and illustrative examples are Byte Watchr analysis. Vendor claims are identified as claims, rather than independent testing.
This article belongs to Byte Watchr’s launch collection. The edition date organizes evergreen coverage and does not imply historical publication. Actual publication is recorded above.
Corrections policy · About this byline