Cybersecurity / News analysis
npm lets trusted publishers manage release tags without long-lived tokens
The new opt-in permission closes a gap in token-free release workflows, but the authority to move a release tag still needs deliberate limits.
THE TOPIC FILE
Authentication establishes who is asking; authorization determines what they can do. Read our coverage of passkeys, recovery, sessions and permissions across personal and enterprise systems.
Cybersecurity / News analysis
The new opt-in permission closes a gap in token-free release workflows, but the authority to move a release tag still needs deliberate limits.
Companies / News analysis
The payment gateway gives participating services a way to charge automated clients per request, creating new requirements for budgets and authorization.
Cybersecurity / News analysis
Private and internal repositories gain more control over where dependency-update jobs execute, including access to specialized environments and private registries.
Cybersecurity / News analysis
A new export brings credential metadata into one view, helping security teams examine access paths while keeping inventory, evidence of use and revocation distinct.
Data Breaches / Explainer
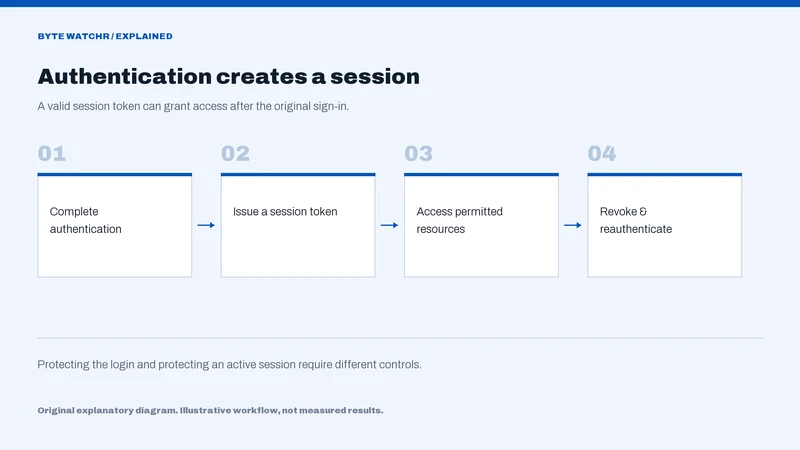
A successful login creates ongoing authority. Protecting that authority requires controls that extend beyond passwords and the moment of multifactor authentication.
Cybersecurity / Explainer
The useful design question is who may perform which action on which resource, under what conditions. Network location supplies context, not automatic permission.
Data Breaches / Analysis
Cloud services can faithfully enforce the wrong permissions. The critical question is which identities can reach data, delegate access, and change the rules.
Cybersecurity / Analysis
Phishing-resistant sign-in is a major improvement. The harder design work begins when a person loses the devices and accounts that hold their credentials.