What to know
- Key establishment and digital signatures serve different purposes.
- An inventory must connect cryptography to an owner and a use case.
- Migration progress should be measured through tested capabilities, not announced intent.
The standards establish a starting point
NIST announced approval of FIPS 203, 204, and 205 on August 13, 2024. They specify ML-KEM for establishing shared secrets and ML-DSA and SLH-DSA for digital signatures. The schemes are designed to resist attacks from future quantum computers.
NIST's migration project separates two workstreams: cryptographic visibility and risk management, including an inventory, and interoperability and benchmarking. That distinction is useful because selecting an algorithm and changing a functioning system are different jobs. This guide does not predict when a cryptanalytically relevant quantum computer will exist.
Source: NIST approval of the first three PQC FIPS · NIST NCCoE post-quantum migration FAQ
Analysis: An algorithm name is not an inventory
A list of libraries can be a useful starting point, but it may not explain what would happen if their cryptographic behavior changed. An actionable inventory connects each use to a purpose, an owner, the systems on either side, and the evidence supporting the entry. Unknowns should remain visible so they can become assigned investigation work.
Consider a hypothetical service with encrypted connections, signed updates, and archived records. Those uses may have different counterparties and change schedules. Replacing a component in one path would not establish that the others have transitioned. The inventory should therefore describe the relationship being protected, not simply count how many applications mention a cryptographic library.
Separate confidentiality from authenticity
Key establishment and signatures address different requirements. NIST describes a key-encapsulation mechanism as a way for two parties to establish a shared secret over a public channel. A digital signature supports checking modification and the identity of a signatory. Treating those as interchangeable would make a migration plan difficult to interpret.
An illustrative planning question is whether an application must protect a conversation, verify a software update, or preserve evidence about an old record. The answers can lead to different tests and operational dependencies. A team should be able to state which requirement a proposed change addresses and which requirements remain outside it. That makes partial progress understandable without overstating it.
Analysis: Prioritize the dependencies that constrain change
A proposed prioritization method can consider how long information must remain protected, how difficult the relevant system is to update, and how many outside parties must coordinate. These are planning dimensions, not a universal ranking formula. A small service with a complicated external dependency might require more preparation than a larger system controlled by one team.
Assigning an owner is particularly useful. If nobody can answer how a device receives updates or who controls a certificate workflow, choosing a target algorithm will not resolve the immediate uncertainty. An early milestone could simply be a documented, verified update path. That is less dramatic than declaring an organization quantum-ready, but it gives the next engineering step something concrete to depend on.
Test the transition as a system change
Interoperability should be demonstrated across the actual components expected to communicate. A local success can leave a partner, intermediary, or older client outside the tested path. NIST's separate interoperability workstream recognizes that this is an engineering problem alongside cryptographic selection.
A useful pilot would identify the intended behavior, the participating versions, the failure conditions, and how results are recorded. It would examine an unsuccessful negotiation as carefully as a successful one. The point is to understand what happens during a mixed transition, rather than to assume every component changes together. Any fallback behavior should receive explicit review because an unnoticed fallback could make a successful connection an ambiguous result.
What a credible roadmap makes visible
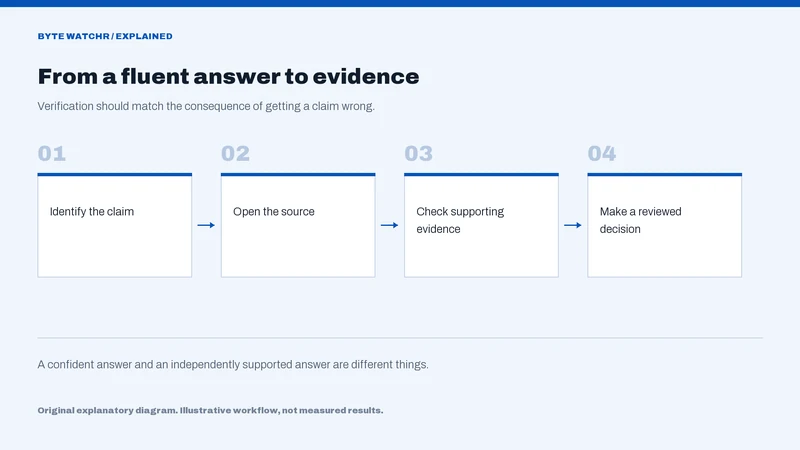
A roadmap should connect dates to observable outcomes: inventory coverage, ownership, a tested integration, or completion for a defined service. It should also distinguish a vendor statement from evidence that the organization's own workflow has changed. This is a proposed reporting structure, not a claim that a particular product is ready.
The standards do not remove implementation errors, operational dependencies, or the need to follow applicable technical guidance. For readers, the most useful question is what the next milestone will prove. A transition becomes easier to assess when each step has a scope, an owner, and evidence, while unresolved systems remain visible. That structure supports progress even when the eventual quantum threat's timing remains uncertain.
Review those assumptions whenever a dependency or ownership arrangement changes.
Sources & further reading
Factual statements are grounded in the linked material. Interpretation and illustrative examples are Byte Watchr analysis. Vendor claims are identified as claims, rather than independent testing.
This article belongs to Byte Watchr’s launch collection. The edition date organizes evergreen coverage and does not imply historical publication. Actual publication is recorded above.
Corrections policy · About this byline