Cybersecurity / News analysis
npm lets trusted publishers manage release tags without long-lived tokens
The new opt-in permission closes a gap in token-free release workflows, but the authority to move a release tag still needs deliberate limits.
THE CYBERSECURITY DESK
The practical systems that protect identities, networks and digital life.
Cybersecurity / News analysis
The new opt-in permission closes a gap in token-free release workflows, but the authority to move a release tag still needs deliberate limits.
Cybersecurity / News analysis
Private and internal repositories gain more control over where dependency-update jobs execute, including access to specialized environments and private registries.
Cybersecurity / News analysis
The internal CryptoLabe tool maps cryptographic dependencies, illustrating why post-quantum planning begins with discovery and validation rather than algorithm replacement alone.
Cybersecurity / News analysis
Canonical’s revised process aims to deliver kernel security fixes more frequently, putting deployment validation and fleet visibility alongside release speed.
Cybersecurity / News analysis
A September advisory described a precautionary response to threat intelligence. The published account did not establish a confirmed compromise or identify a specific vulnerability.
Cybersecurity / News analysis
A new export brings credential metadata into one view, helping security teams examine access paths while keeping inventory, evidence of use and revocation distinct.
Cybersecurity / News analysis
The September announcement connected an infrastructure operation with notification and remediation, two parts of the story that deserve separate measures of progress.
Cybersecurity / Analysis
Replacing permanent application keys can reduce exposure. The remaining work is to secure credential issuance, limit authority, and make the entire lifecycle observable.
Cybersecurity / Explainer
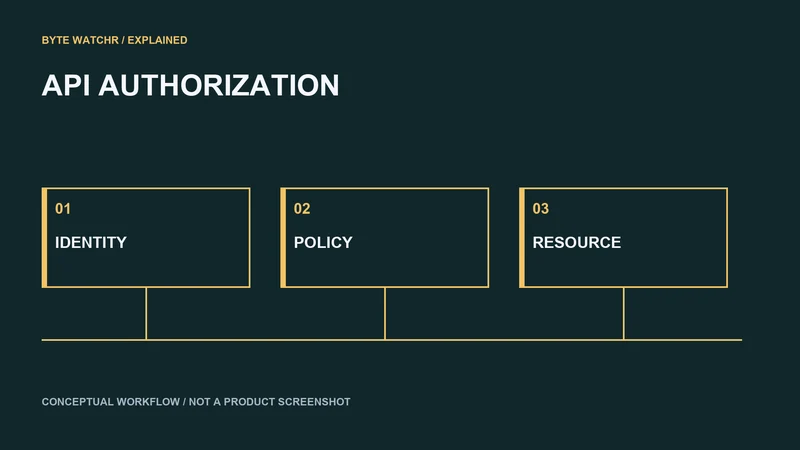
The useful design question is who may perform which action on which resource, under what conditions. Network location supplies context, not automatic permission.
Cybersecurity / Explainer
A valid login does not prove that a caller may read or change a particular object. APIs need permissions that follow the record, action, and relevant fields.
Cybersecurity / Analysis
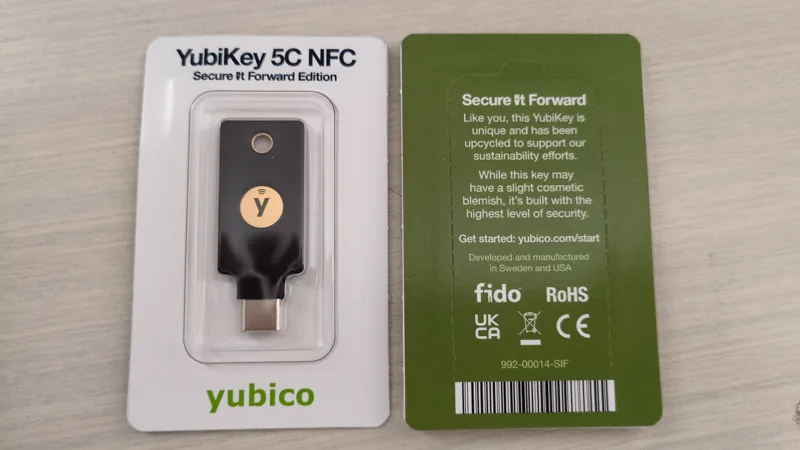
Phishing-resistant sign-in is a major improvement. The harder design work begins when a person loses the devices and accounts that hold their credentials.
Cybersecurity / Field guide
A successful backup job measures copying. Ransomware readiness requires evidence that people, systems, and trusted data can come back together.